Every completed document carries a fingerprint of the final PDF. With one click you can check that the file on your site is exactly the file that was sealed when the last person signed.
This is what you rely on if someone ever says "that is not what I signed".
What a SHA-256 seal is:
SHA-256 turns a file into a 64 character code, its fingerprint. The same file always gives the same code. Change one letter anywhere in the file and the code is completely different. The code cannot be turned back into the file.
When the last signer signs, ResultsAiX Sign takes the fingerprint of the finished PDF and stores it with the document. That is the seal.
Where to find it:
Open AiX Sign, the Documents tab, and click a completed document. The Sealed SHA-256 shows under the buttons. Uploaded documents also show the Original file SHA-256 of the PDF you uploaded.
Using Verify Integrity:
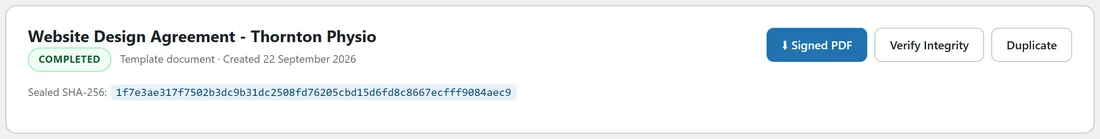
- Click Verify Integrity on the completed document.
- The line under the buttons reads Recomputing SHA-256... for a moment.
- The result appears in its place.
What the result means:
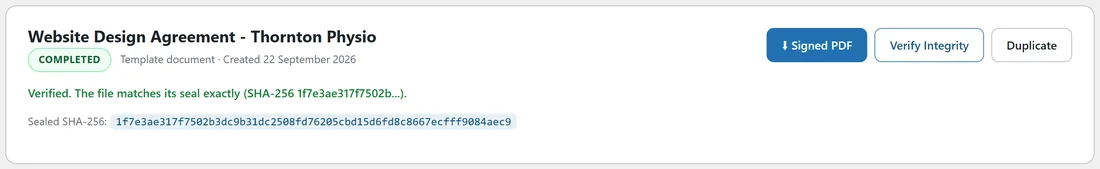
- Verified. The file matches its seal exactly, followed by the start of the fingerprint: the stored PDF is unchanged since sealing.
- A line saying the stored file does not match the recorded seal: the stored file has changed since sealing, for example through a restore from an old backup or a migration tool. Use the copy from the completion email, which was sent at the moment of sealing.
The two fingerprints:
- The sealed fingerprint covers the whole final PDF file. It is stored on your site and printed in the completion email.
- The evidence hash is printed inside the Certificate of Completion. It is built from the agreed text, the original file's fingerprint for uploads, each signer's name, email, signing time and IP address, and the signature images.
A file cannot contain its own fingerprint, which is why the file fingerprint lives in the email and on your site, and the evidence hash lives inside the certificate.
If someone produces a different copy:
- Open the document and click Signed PDF to download your stored copy.
- Click Verify Integrity to confirm your stored copy matches its seal.
- Open the Certificate of Completion and point to the consent time, first view time, signing time, IP address and device of the signer.
- Ask for their copy and run any SHA-256 tool on it, or compare it with the fingerprint in the completion email. A copy with a different fingerprint is not the file that was sealed.
Keeping your records safe:
Signed documents live on your own site, so your website backups now hold your signed contracts. Back up the site regularly and keep the backups somewhere safe. See Where Documents Are Stored, And Privacy.
A real example:
Months after the Thornton Physio website went live, Sam opened the agreement and clicked Verify Integrity. The line read Verified. The file matches its seal exactly (SHA-256 1f7e3ae317f7502b...), the same start as the fingerprint in Mia's completion email.
Tips:
- Run Verify Integrity after moving your site to a new host.
- Keep the completion emails. They carry the same fingerprint as your stored file.
- On Windows you can check a file's fingerprint in PowerShell with Get-FileHash. On a Mac, use shasum -a 256 in Terminal.